The following posting is an opinion piece. It's based on personal experiences and anecdotal information. deal with it.
So your organization is looking to hire one or more Information Security Professionals. Maybe you are growing your InfoSec organization, adding to your IT organization, or realizing that, yes, you need to create an InfoSec group. (all those big breaches in the news have you running scared)
Do you have a good idea of what you need in terms of skills, knowledge, and experience? Do you have a good idea what kind of role you are trying to fill? Do you have an idea of salary candidates with the skills you need are expecting? You best figure this out soon. (hopefully you've consulted with professionals to help you out, and I don't mean recruiters.) Here are some things to consider.
Now, a word of warning. It may seem that I am stating the obvious at several points, and in a condescending manner. But the sad thing is that in speaking with recruiters and HR people is that they don't seem to understand these points. As an infosec professional, this p*sses me off, and so I feel I need to state the obvious for those who don't get it.
Showing posts with label career. Show all posts
Friday, January 30, 2015
Friday, November 14, 2014
Is your company causing the IT Skills gap?
I've posted previously on the "IT/IS Skills Gap". As I'm previously noted, I'm not convinced it's necessarily due to a lack of skilled people, but in how some companies are handling filling positions.
A recent article at CSO magazine is interesting.
Monday, November 10, 2014
Is the Information Security Skills Gap misidentified?
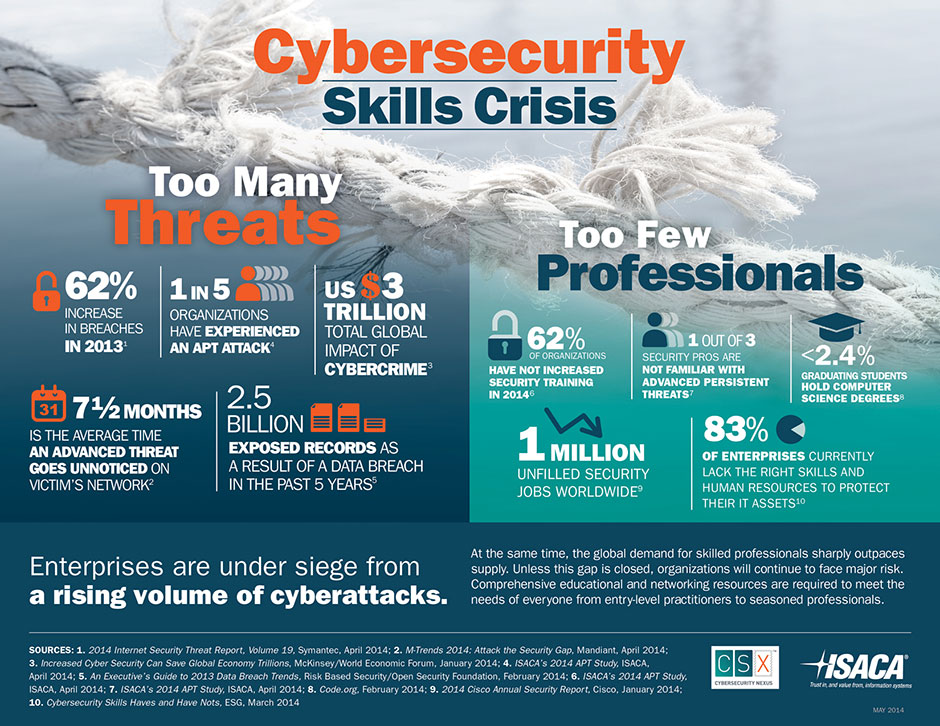
In recent postings, I've touched on the information security skills gap. Many individuals and groups are pushing the idea that the large number of unfilled information security positions (40% is a number I've seen tossed around) is due to a "skills gap", that there are not enough skilled individuals to fill them. And so we need to pump out more infosec professionals.
As noted, I'm not in agreement with this idea. There may be a skills gap in certain areas and in certain markets, but don't think its correct to say we have an overall skills gap.
Thursday, November 6, 2014
ISSA's Cybersecurity Career Lifecycle
At the recent ISSA International Conference in Orlando, they rolled out a new program, the Cybersecurity Career Lifecycle (CSCL).
The CSCL is meant to be an industry-wide initiative to bring a level of professionalism. It defines and maps the five stages of the cybersecurity career lifecycle. For each of these stages, the framework defines the knowledge, skills, aptitudes and responsibilities, thereby allowing cybersecurity professionals to identify the current stage of their career.
The first stages are:
Article on it at Security Week.
The CSCL is meant to be an industry-wide initiative to bring a level of professionalism. It defines and maps the five stages of the cybersecurity career lifecycle. For each of these stages, the framework defines the knowledge, skills, aptitudes and responsibilities, thereby allowing cybersecurity professionals to identify the current stage of their career.
The first stages are:
- pre-professional (students, young adults),
- entry level (1-2 years)
- mid-career (3-7 years)
- senior level (7+ years)
- executive level (12+ years)
More is coming, and this looks very interesting.
Article on it at Security Week.
Tuesday, November 4, 2014
Is there an IT Security Skill Set Gap??
Over the last year or so, I have heard from several sources that we have a "cybersecurity skills gap". That we have more IT security positions then we have skilled people to fill them.
Here is one example of such claims:
Now, as an experienced cybersecurity professional who has been on the job market for some time without too much success, I have a hard time accepting this. Why do I say this?
Here is one example of such claims:
Now, as an experienced cybersecurity professional who has been on the job market for some time without too much success, I have a hard time accepting this. Why do I say this?
Subscribe to:
Posts (Atom)